
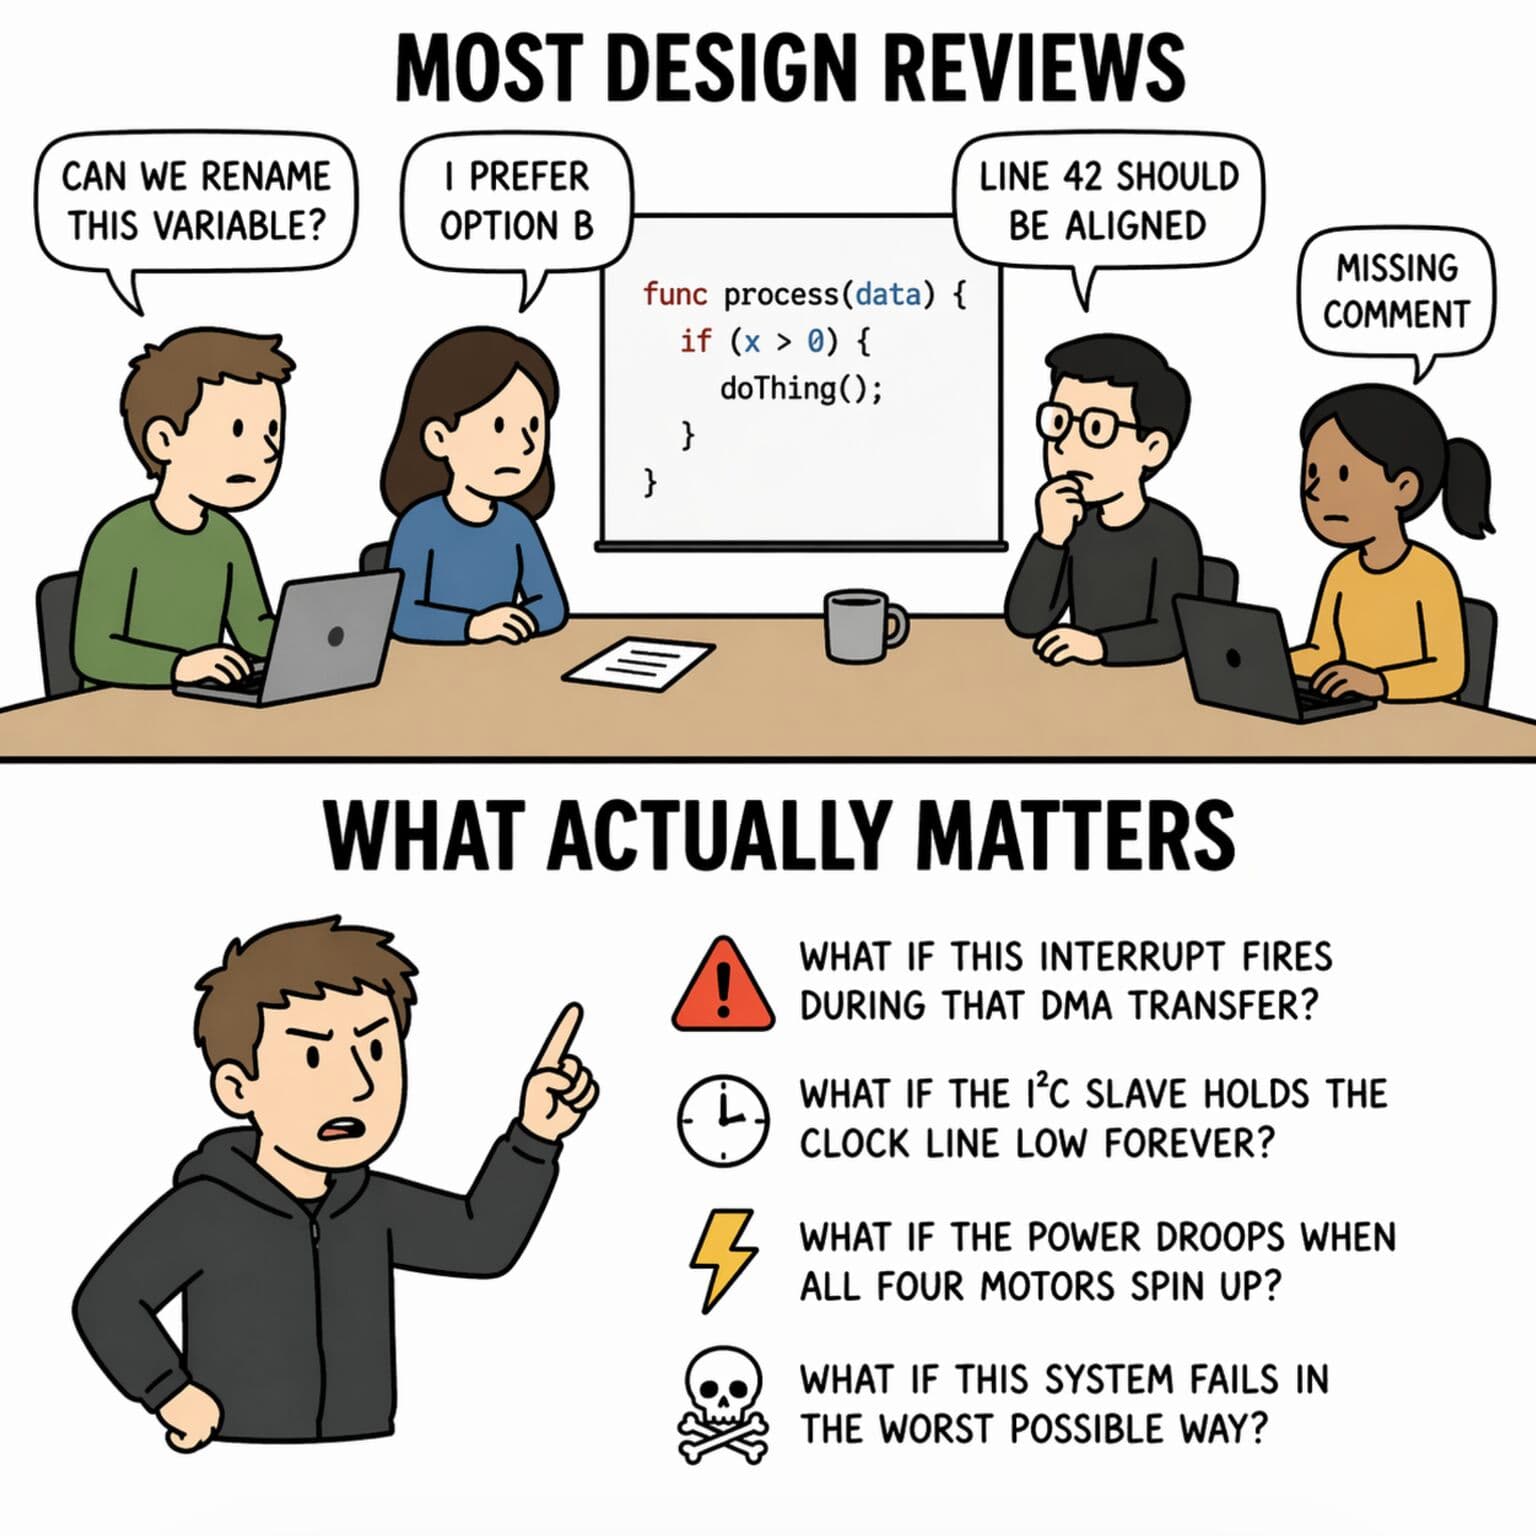
Most design reviews miss the bugs that actually kill products.
They argue about variable naming. They bikeshed function signatures. They catch formatting issues that the linter would flag in ten seconds.
Meanwhile, nobody asks: what happens if this interrupt fires while we're halfway through that DMA transfer? What if the I²C slave holds the clock line low forever? What if the power supply droops when all four motors spin up simultaneously?
Design reviews have become social rituals that signal diligence without delivering it. Real review requires asking the questions that feel paranoid. The questions that start with "what if this system fails in the worst possible way?"
The polite questions are safe. The paranoid questions save you from recalls.
What is the stupidest bug you have seen sail through multiple reviews?
#EmbeddedSystems #FirmwareDevelopment #HardwareDevelopment #CodeReview #DesignReview #Debugging #EmbeddedEngineering #EngineeringCulture